Audit log
Every call, decision and admin change, in a tamper-evident log you can verify and export.
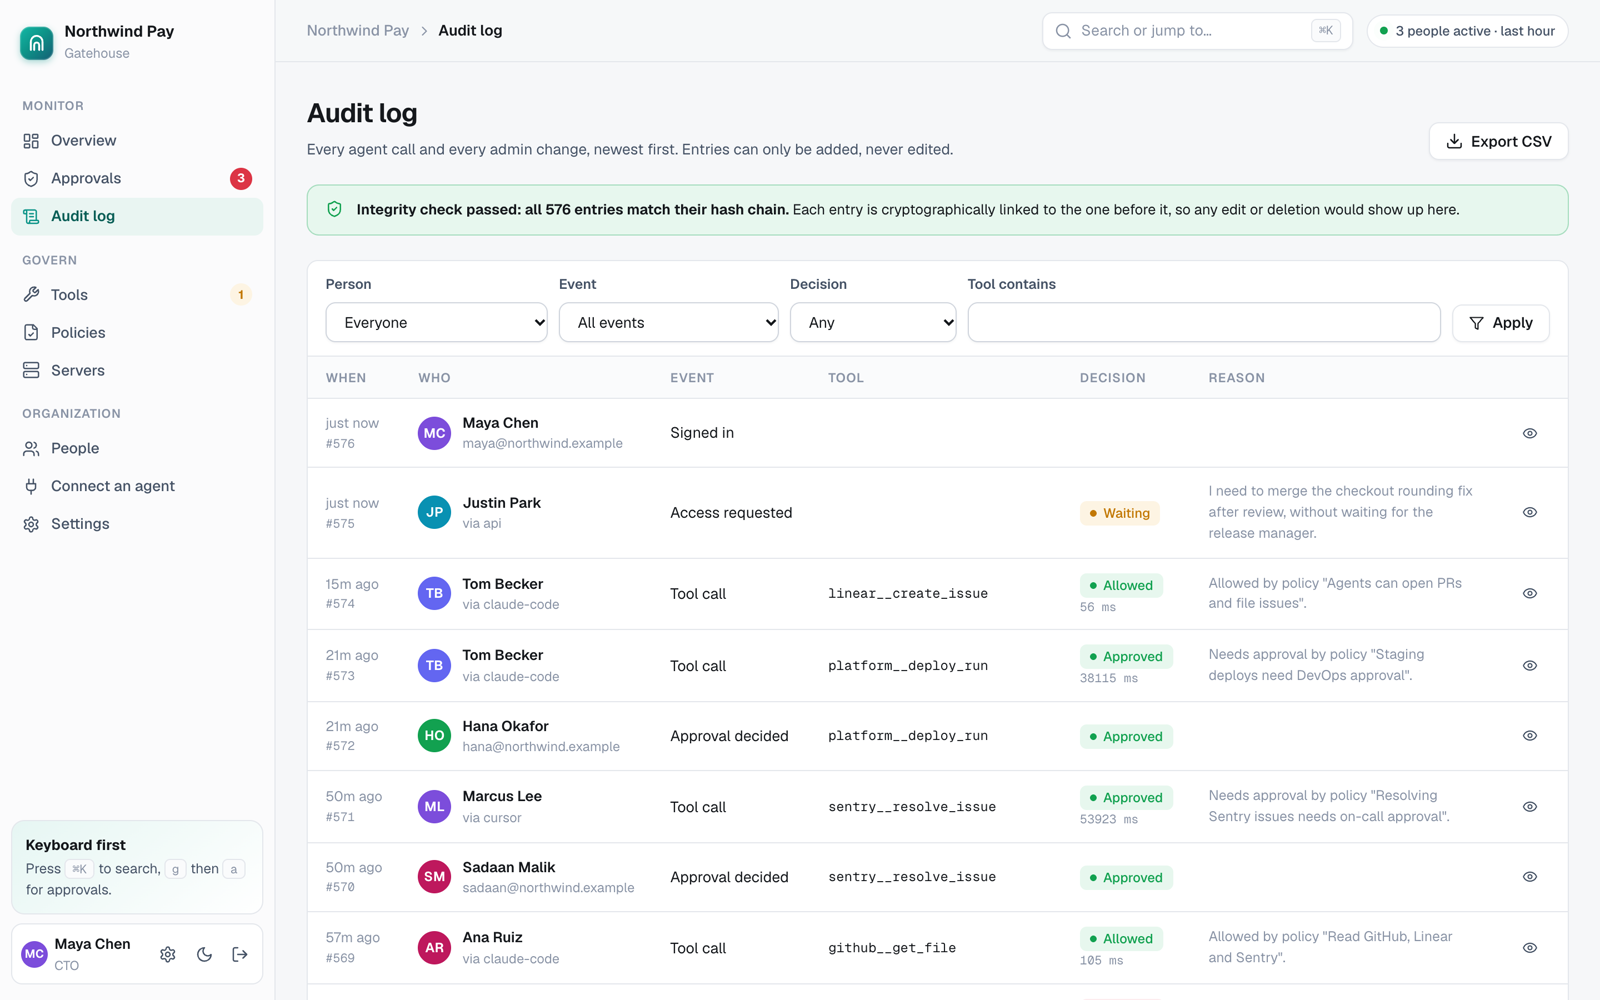
The Audit log records every tool call, policy decision, approval, access request, sign-in and admin change.
What each entry holds
- When it happened and who did it.
- Which agent (client name and token).
- What: the tool, the decision, and the policy behind it.
- Details: arguments with secrets redacted, the result size, duration and any error.
Members see their own activity. Admins, owners and auditors see everyone's.
Set GATEHOUSE_AUDIT_ARGS=hash to keep only a hash of each call's arguments instead of the redacted arguments.
Tamper evidence
Each entry stores a SHA-256 hash of its contents plus the previous entry's hash, forming a chain. The database also refuses updates and deletes on the audit table. If someone edits or removes an entry with raw database access, the chain breaks at that point.
Check the chain any time:
- Console: the integrity badge at the top of the Audit log.
- CLI:
npm run cli -- verify-audit - API:
GET /api/audit/verify
Search and export
Filter by person, event type, decision or tool name. Export CSV downloads the filtered view for a review or an auditor.
For a SIEM, use audit streaming to send every entry as it's written.